
Security Practice, Stated Plainly
How people sign in, who can open what, how data is encrypted and backed up, and how to report a problem.How people sign in, who can open what, how your data is encrypted and backed up, and how to tell us about a problem. Each practice here is one you can see working in the app.
How We Keep Programme Data Secure
Sign-in that guards every account
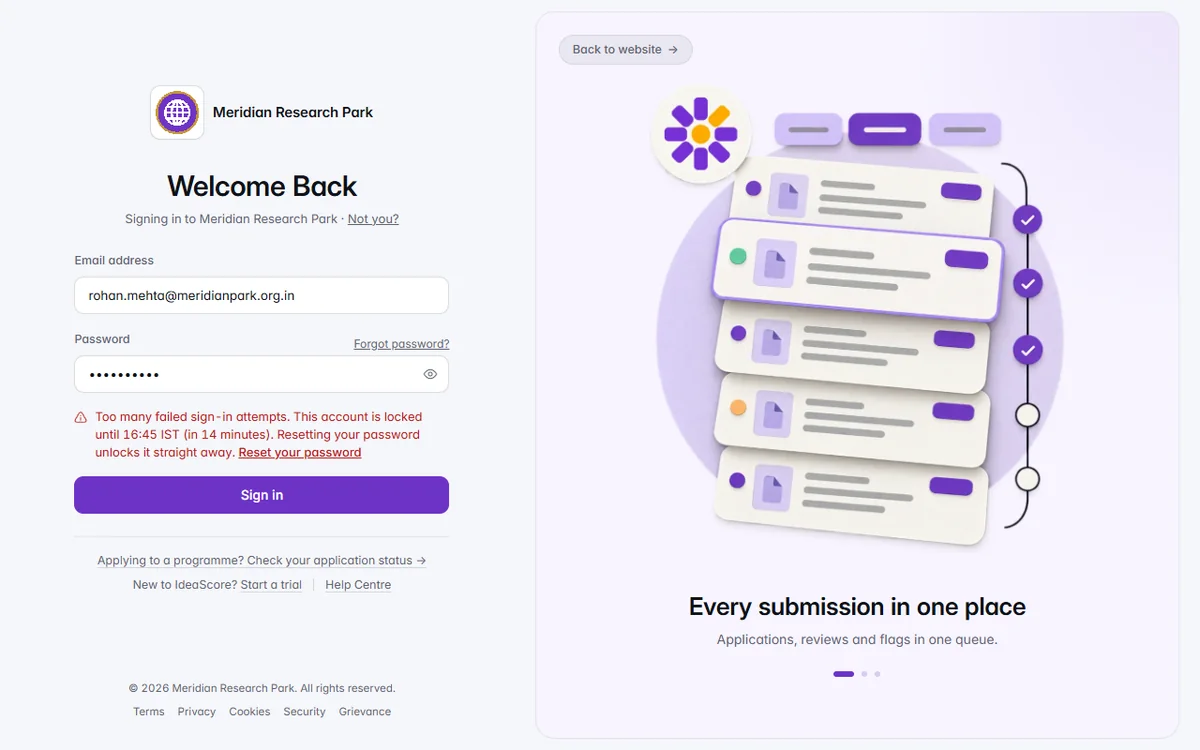
Google or Microsoft sign-in, or your own domain on Enterprise. After too many wrong passwords, sign-in pauses and says when it opens again.People sign in with Google or Microsoft where your organisation allows it, and it only ever signs in someone you have already added. On Enterprise, owners can require staff to use your organisation's Google Workspace or Microsoft Entra domain, with a preview of who is affected first; applicants are never affected. After too many wrong passwords, sign-in pauses for a while and says when it opens again, and a password reset is the quick way back.
Roles that open exactly what they should
Built-in and custom roles, for the organisation or one programme. Private files open only for staff, assigned evaluators and the team; shared links expire.Owner, programme admin and evaluator are built in, and a custom role is a name and the permissions you tick, for the whole organisation or for one programme. A role sees the pages and programmes its permissions cover, and nothing more. Pitch decks, agreements and other uploads open only for programme staff, the assigned evaluators and the team itself, and links shared outside the app expire.
Encrypted in transit, at rest and in every backup
HTTPS with HSTS, disks encrypted at rest, and a nightly backup encrypted with AES-256-GCM before it leaves the server.Every page and API call uses HTTPS, and browsers are told with HSTS never to fall back to an unencrypted connection. Our database and storage providers encrypt the disks that hold your data. Every night each organisation is backed up, encrypted with AES-256-GCM before it leaves the server, checked after it is written, and stored away from the servers that run the app.
Export everything, whenever you need it
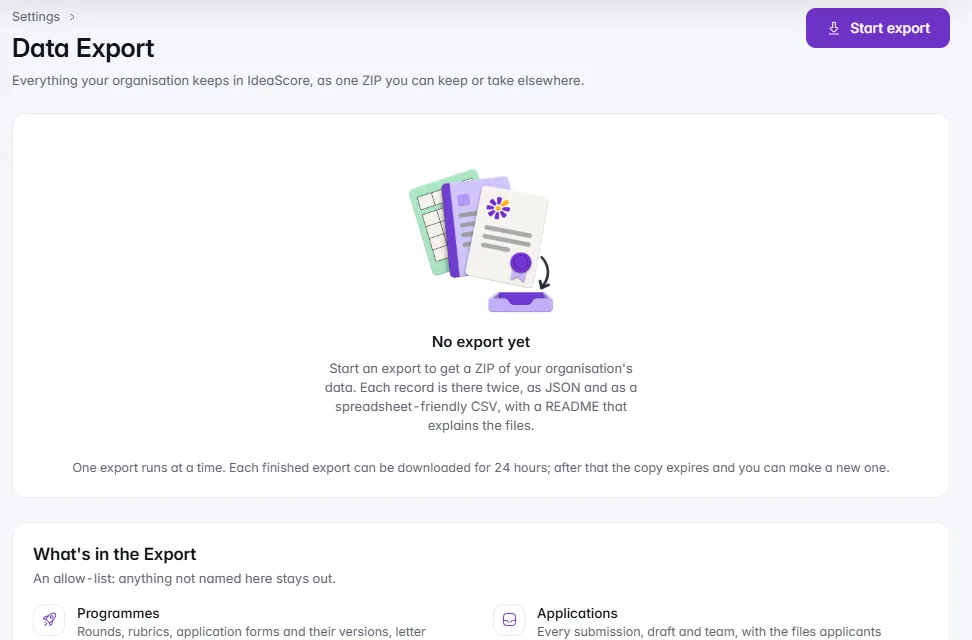
The whole organisation as one ZIP at any time, and for 90 days after a plan ends. Secrets never leave in an export.Owners export the whole organisation as one ZIP at any time: programmes, applications, scores, decisions, people, the audit log and files, each record as JSON and as a spreadsheet-friendly CSV, with a README. After a plan ends you have 90 days to take it with you. Passwords, sessions, two-step secrets and API keys never leave in an export.
Security Posture answers your IT team from your own settings
Two-step sign-in, single sign-on, backups and sign-ins, answered from your own settings. Copy for your IT team gives you a plain-text summary.Security Posture, first under Settings, answers what a buyer's IT team asks first: two-step sign-in, single sign-on, backups and sign-ins, one tile each, with how many are in place at the top. Choose a tile for the answer, its evidence and the setting to change. Copy for your IT team copies a plain-text summary for an email or a security questionnaire.
Safeguards That Run Quietly
Rate limits
Checked on the server
Secrets kept out of the code
An audit log in plain sentences
Signed webhooks
Your own infrastructure, if you need it
Found a Problem? Tell Us
We welcome reports from security researchers, and we answer every one.
Write to us
We acknowledge it
Give us time
Built to Keep Your Data Safe
14laws and standards we work to
- 5
- data and IT laws
- 9
- security and access standards
- 3
- regions: India, EU, US
Privacy, IdeaScore AI and the Standards We Work To
What IT Teams Ask First
Questions Your IT Team Wants Answered?
A product specialist can walk your IT team through sign-in, roles, backups and Security Posture, with your questionnaire beside you.